


Scale Security Without the Extra Overhead
Financial institutions operate under some of the most demanding regulatory requirements while accelerating cloud adoption for digital banking, payments, and customer experience.
PCI DSS, SOX, NIST, CIS, FFIEC. Overlapping frameworks with continuous audit requirements. Point-in-time compliance isn't enough when examiners expect continuous evidence.
Cardholder data, PII, financial records. A single misconfigured storage bucket or overpermissive access policy can trigger a breach notification, regulatory action, and reputational damage.
Hundreds of cloud accounts across lines of business. Development teams shipping daily. Cloud footprint growing faster than security teams can review and remediate manually.


Trusted by financial services organizations
How Financial Services Use Turbot Guardrails
Continuous Regulatory Compliance
Enforce PCI DSS, SOX, and SOC 2 controls continuously across every cloud account. Automated evidence collection and real-time posture tracking for examiners and auditors.
- ✓14,000+ policies mapped to regulatory frameworks
- ✓Continuous compliance, not point-in-time audits
- ✓Consistent posture across all environments
Data Protection & Access Control
Prevent data exposure before it happens. Guardrails enforces encryption, blocks public access, and manages IAM policies automatically across your cloud accounts.
- ✓Automated encryption enforcement at rest and in transit
- ✓Block public access to sensitive resources
- ✓Least-privilege IAM policy enforcement
Multi-Cloud Enterprise Security
Manage hundreds of cloud accounts across AWS, Azure, GCP, OCI, and GitHub with a single policy hierarchy. Consistent security posture across all lines of business.
- ✓One platform for all clouds and accounts
- ✓Policy inheritance across the organization
- ✓Multi-region and data residency controls
Enable Innovation Under Control
Let development teams ship faster without compromising security. Self-service cloud access with automated guardrails means teams build and deploy within approved boundaries.
- ✓Speed without compromise on security or compliance
- ✓Automated boundaries that don't require tickets
- ✓Accelerate cloud adoption without increasing risk
Preventive Security for Financial Services:
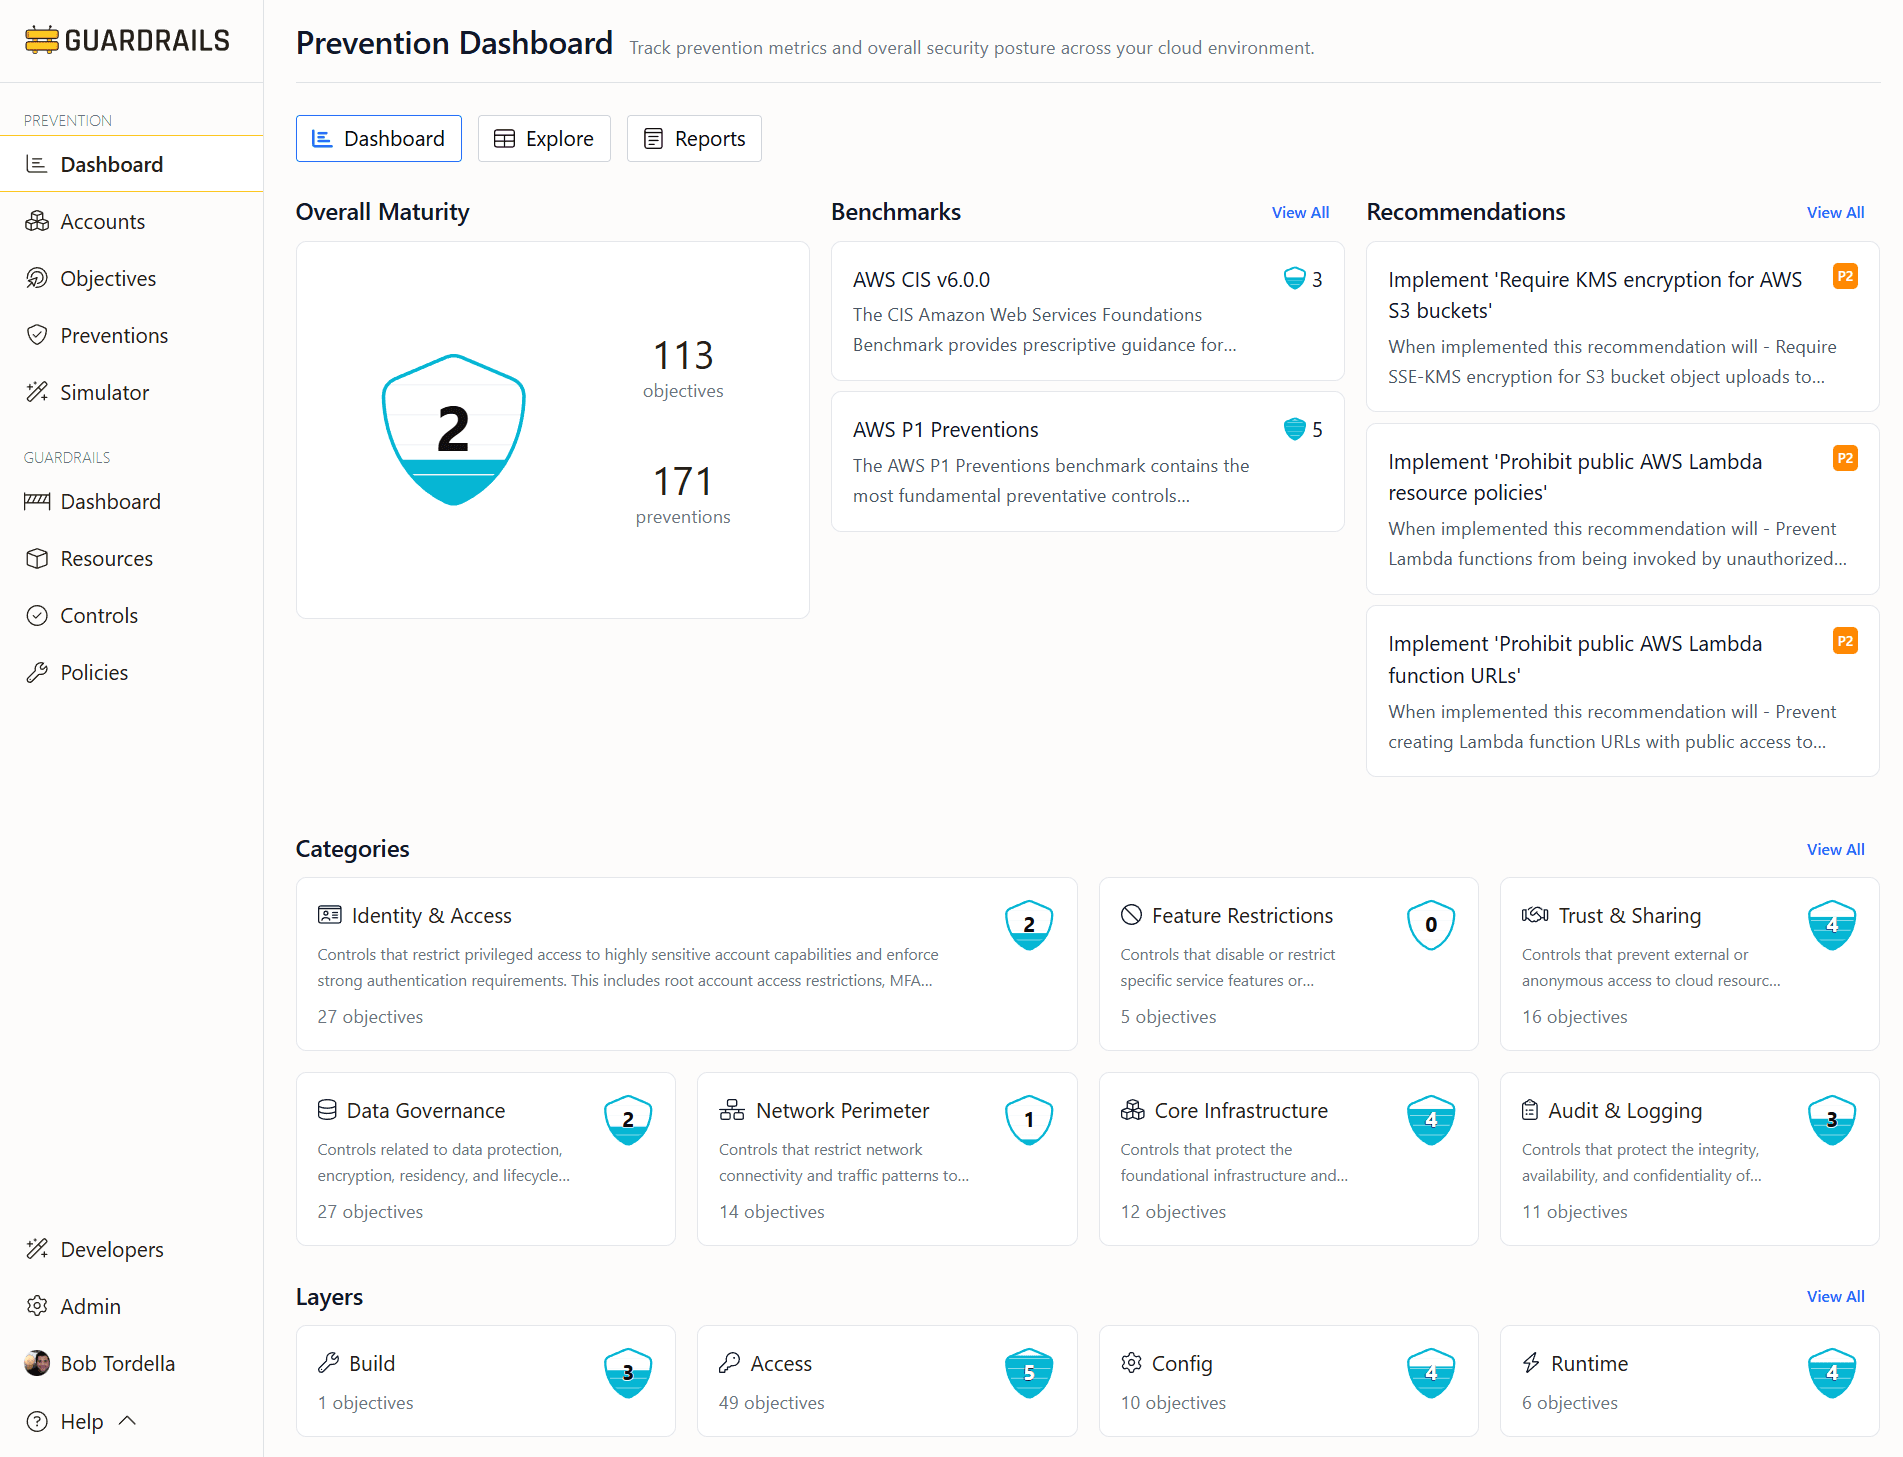
Visualize and improve your preventive posture
See exactly what preventive controls are in place across your cloud organization and where the gaps are. Guardrails maps your policies, scores your coverage, and recommends the highest-impact controls to deploy next.
Benchmark against PCI DSS, SOX, SOC 2, NIST, and CIS frameworks. Track improvement over time and demonstrate progress to leadership and auditors.
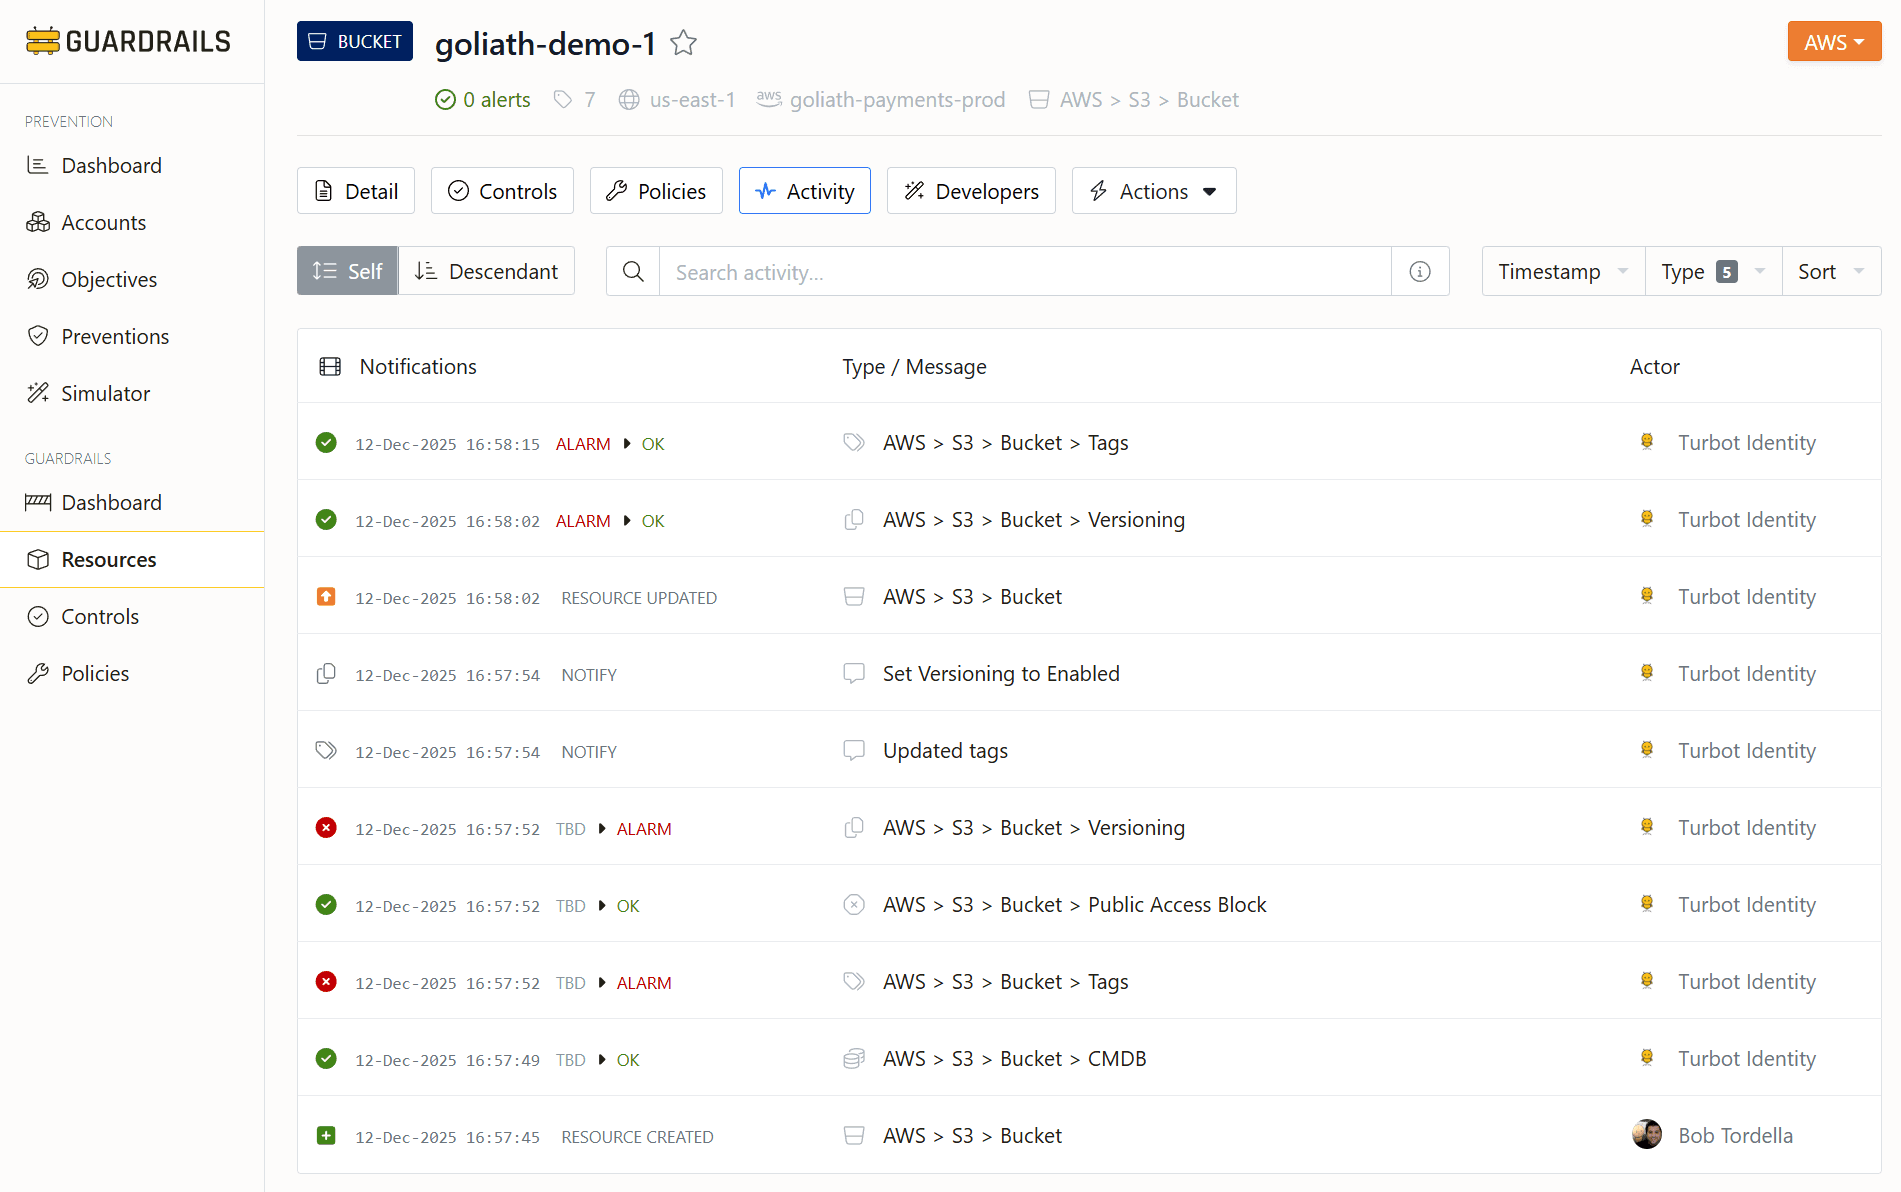
Auto-remediate misconfigurations
Unencrypted storage, public endpoints, overpermissive IAM. Guardrails detects and fixes these automatically. No tickets, no waiting, no exposure window.
Runtime prevention runs 24/7 across all accounts and clouds. Misconfigurations are corrected in minutes, not days.

Simulate and test before enforcement
In regulated financial environments, unplanned disruptions are unacceptable. Simulate new preventive controls against your actual environment before deploying.
See exactly which resources would be affected. Validate that controls won't disrupt trading systems, payment processing, or customer-facing applications, then roll out with confidence.
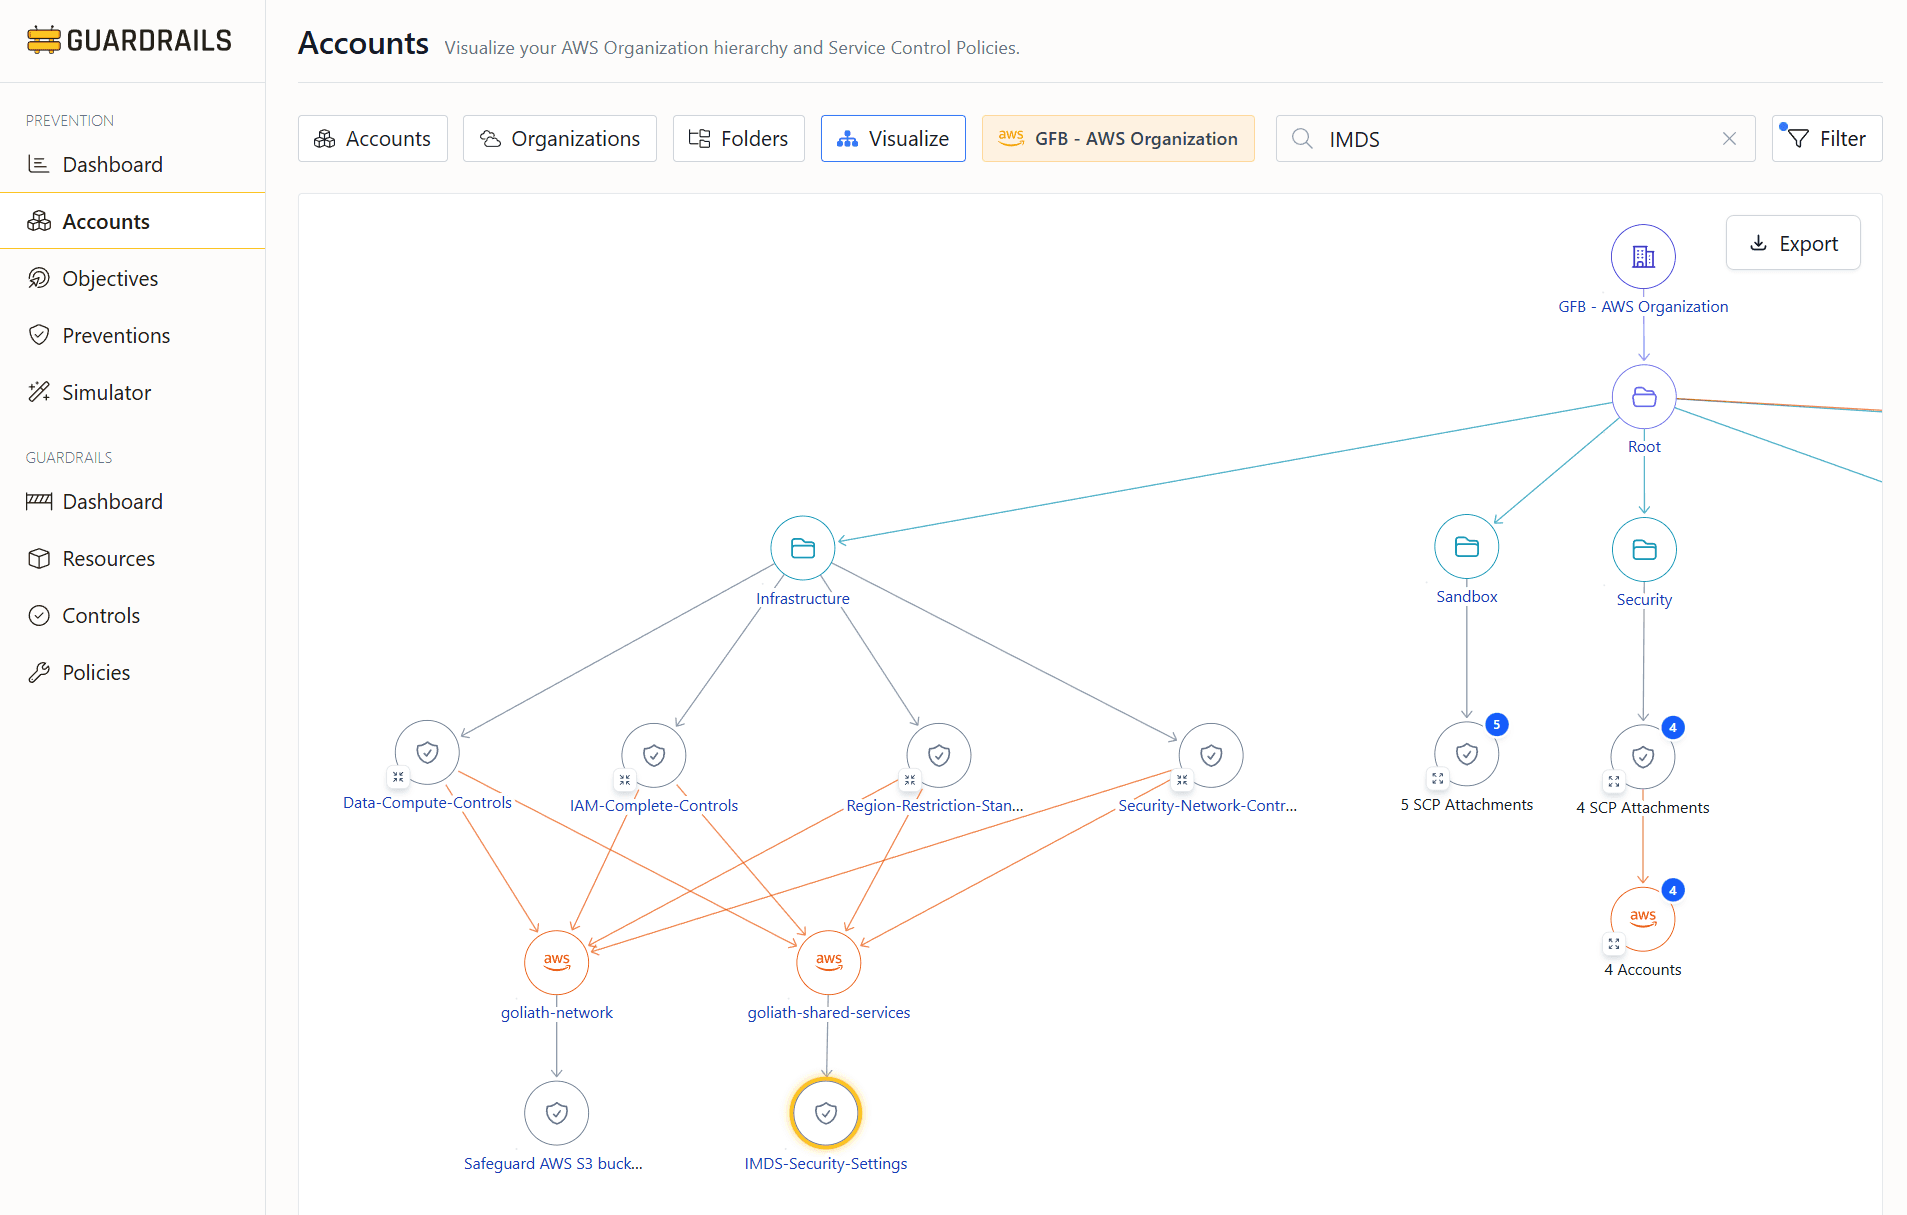
Complement your CNAPP with prevention
Your CNAPP or CSPM finds problems. Guardrails prevents them from happening in the first place and auto-corrects the ones that slip through. Add a prevention layer to reduce the volume of findings your team has to triage.
Works alongside Wiz, Prisma, CrowdStrike, Tenable, and other visibility tools. Prevention reduces volume, detection catches what remains.
Add a Prevention Layer to Your Stack
Your CNAPP and CSPM tools provide visibility, scanning resources and surfacing risks. Guardrails works upstream, blocking non-compliant resources at creation time and auto-remediating drift so fewer issues reach the scanner.
Together, they create defense in depth: prevention reduces volume, detection catches what slips through. Your security team spends less time on remediation and more time on the work that drives value.
How Guardrails works with CNAPP tools →Usage-Based Pricing That Scales with Your Organization
Pay per resource, per control, per month. Turn controls on or off as needed. Start with a few accounts and expand across your organization as you go.
Per resource, per control. A resource with tagging and encryption enforcement costs $0.10/month.
Start with a few controls and expand. Add enforcement as your cloud footprint grows. Costs flex with your environment.
Try Guardrails on your own cloud accounts. We'll help you get set up and see the value before committing.